An unidentified hacker, believed to be a Chinese speaker, leveraged artificial intelligence-powered tools to infiltrate several financial institutions in South Korea and extract sensitive data. According to a report from the US-based cybersecurity firm CrowdStrike, these cyberattacks occurred during a window between late September and early October.
The perpetrator reportedly utilized ARTEX, an open-source penetration-testing tool developed in China, in conjunction with large language models to bypass banking security systems. Specific targets identified in the campaign included a loan inquiry service at one bank and a mobile-support platform designed for employees at another lender. Investigators from CrowdStrike managed to link two servers to the activity, one of which was located in Hong Kong.
While the exact identity of the attacker remains unconfirmed, the firm noted that the individual appears to be financially motivated. This assessment is based on observed searches for online marketplaces that facilitate the sale of stolen South Korean data. Despite these findings, the full extent of the breaches and the total volume of information compromised have not yet been determined.
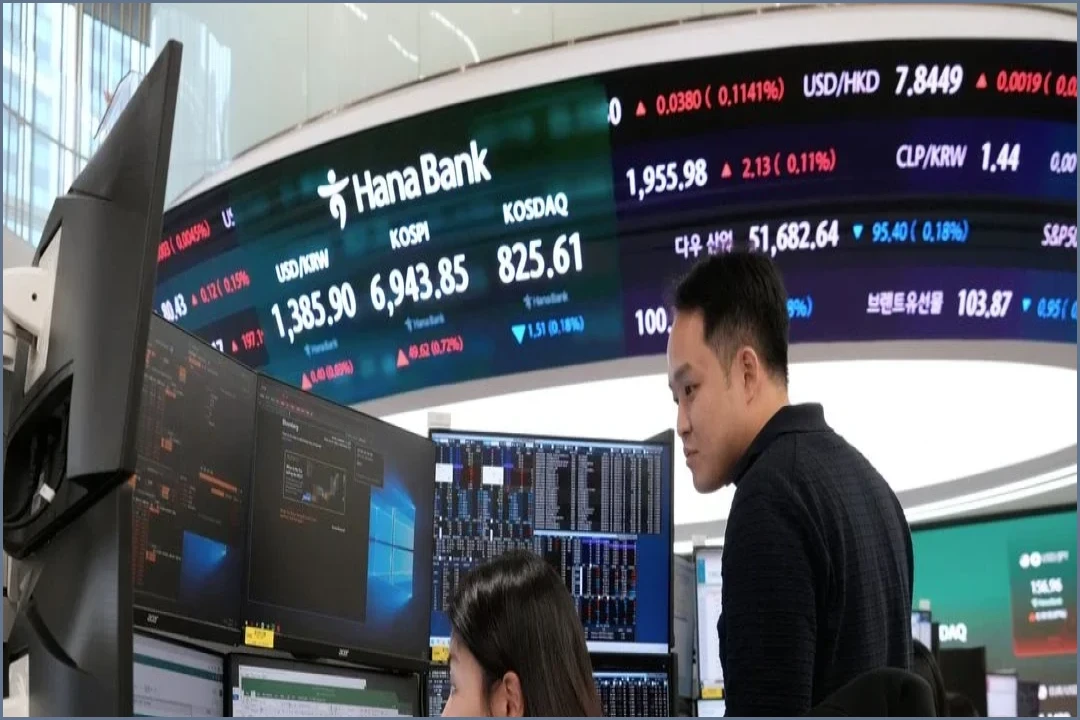
These security incidents follow a series of previously reported data breaches involving Hana Bank, KB Kookmin Bank, and Shinhan Bank. Those events have already triggered formal investigations by financial regulators and law enforcement authorities in the region.